Running Ronne
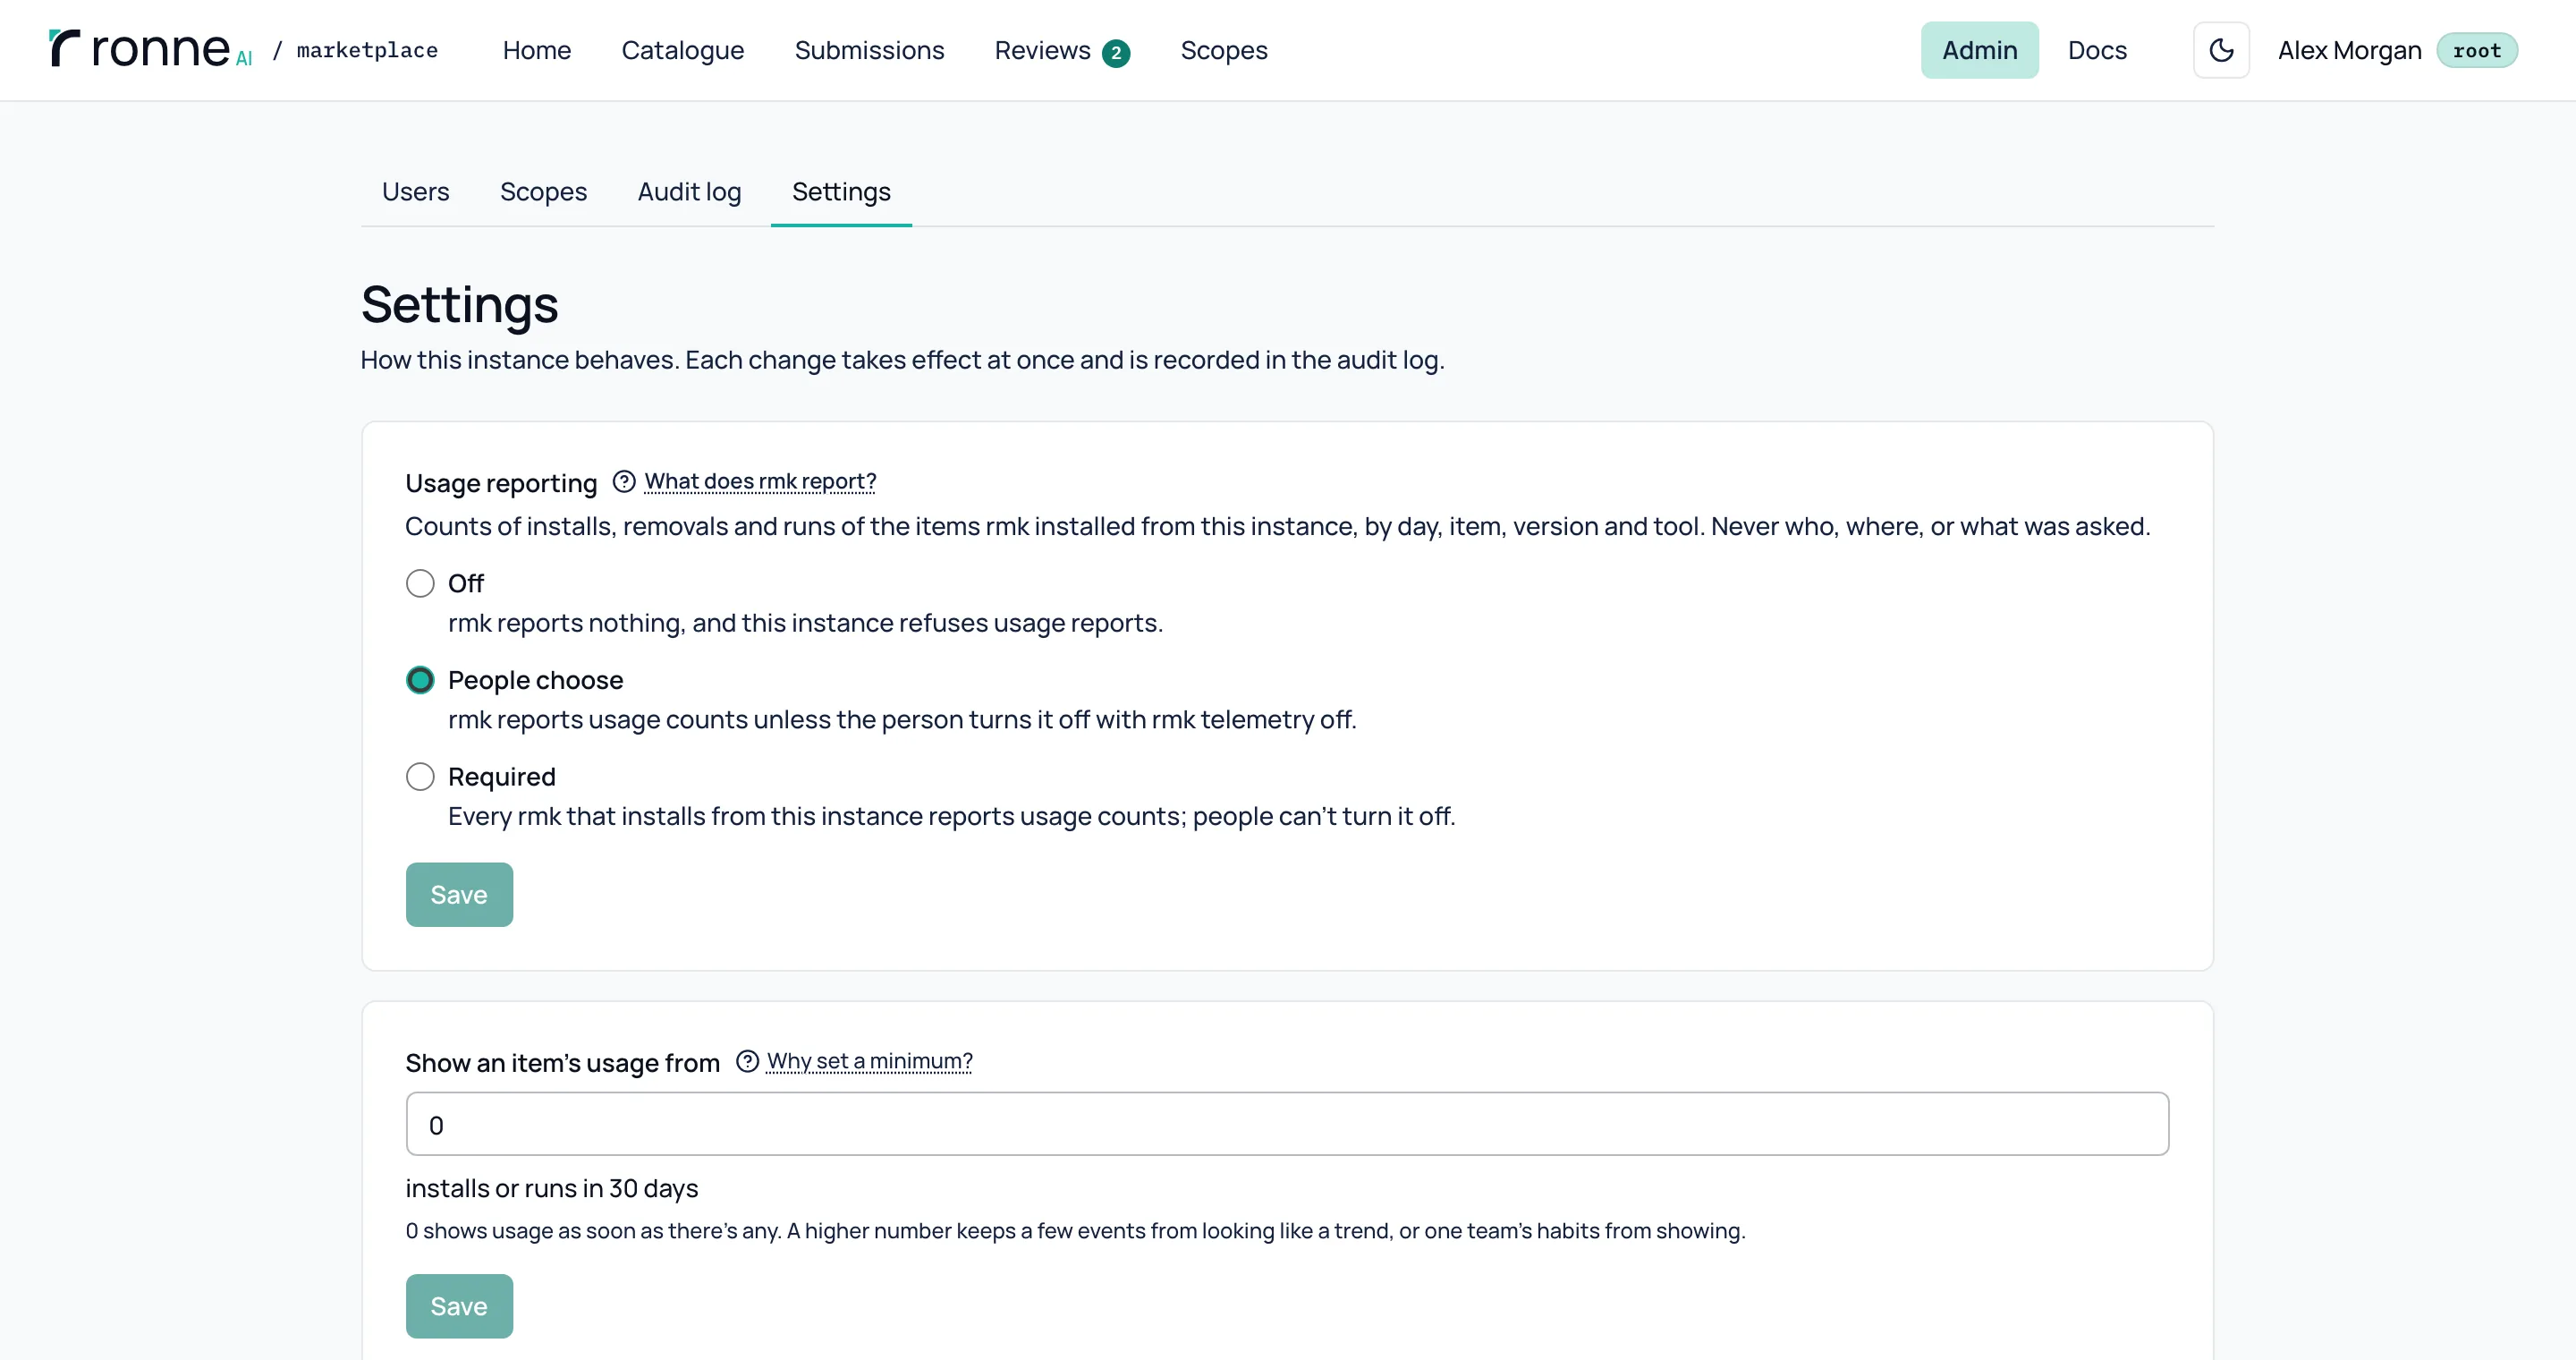
Screenshots of version 0.5.0, running on a new instance with the sample items from the repository. The people in them are sample accounts, and the usage counts are simulated. The identity provider in them is a stand-in made for tests.
Backups, logs and telemetry
rmk-server backup writes one archive of the database, the stored items and the settings file while Ronne runs; --verify checks it and restore brings it back, on the same machine or another. The server writes one JSON line per event, with the request it belongs to and never a secret. Metrics and traces go to an OpenTelemetry collector only if you point the server at one.
$ pnpm run backup --out <backups folder> --yes
Wrote <backups folder>/ronne-backup-20261020-204036.tar (607 KiB) in 0.0 s.
2,968 rows in 35 tables, 16 stored files (7 KiB).
! It holds the settings file, with AUTH_SECRET and the database's password: keep it as safe as the server itself, and use --encrypt for copies that leave this machine.
! STORAGE_PATH comes from the environment and isn't in this backup.

$ pnpm run backup --verify <archive>
ronne-backup-20261020-204036.tar is complete: every checksum matches, and every released version's artifact is in it.
Made by Ronne 0.5.0 at 2026-10-20T20:40:36.894Z from SQLite, 31 migrations applied (607 KiB).
2,968 rows in 35 tables, 16 stored files (7 KiB), with the settings file.
! Not in it, as they came from the environment: STORAGE_PATH.

$ pnpm run restore <archive> --yes   (into a second, empty data folder)
Restored 2,968 rows in 35 tables and 16 stored files from ronne-backup-20261020-204036.tar (made by Ronne 0.5.0 at 2026-10-20T20:40:36.894Z from SQLite) into the SQLite database.
! Wrote a settings file with a new AUTH_SECRET (not the backup's: run with --with-settings for that), so everyone signs in again.
Next, start the server: pnpm dev, or pnpm start after pnpm build.{"time":"2026-10-20T20:40:49.115Z","level":"info","msg":"Access token issued","domain":"identity","event":"token.exchanged","requestId":"01M5DGQ6629QT5AMV0FGJ0CKWB","userId":"01M5DG4FKEPH4D7JQ4AR11QFYY"}
{"time":"2026-10-20T20:40:49.180Z","level":"info","msg":"Draft uploaded","domain":"submissions","event":"draft.uploaded","requestId":"01M5DGQ677G9KEC0JAPHK2C9E2","userId":"01M5DG4FKEPH4D7JQ4AR11QFYY","files":2,"bytes":489}
{"time":"2026-10-20T20:40:50.128Z","level":"info","msg":"Released","domain":"submissions","event":"version.released","requestId":"01M5DGQ75PQDZC2SJDE1ATMY5P","userId":"01M5DG4FKEPH4D7JQ4AR11QFYY","count":1}
{"time":"2026-10-20T20:40:53.314Z","level":"info","msg":"Request handled","domain":"http","event":"http.request","requestId":"01M5DGQA9Z8Y2AKHNE9K8D402D","userId":"01M5DG4FKEPH4D7JQ4AR11QFYY","method":"GET","route":"/api/v1/workspaces/[workspace]/items/[scope]/[name]/[version]/tarball","status":200,"ms":2}Usage counts, if root wants them
Root decides whether rmk and the MCP server report installs and runs: off (the default), people choose, or required. Only daily counts per item, version and tool are kept, for 90 days, never who ran what or where.
Want to try it? Run the Docker image, or read the code.